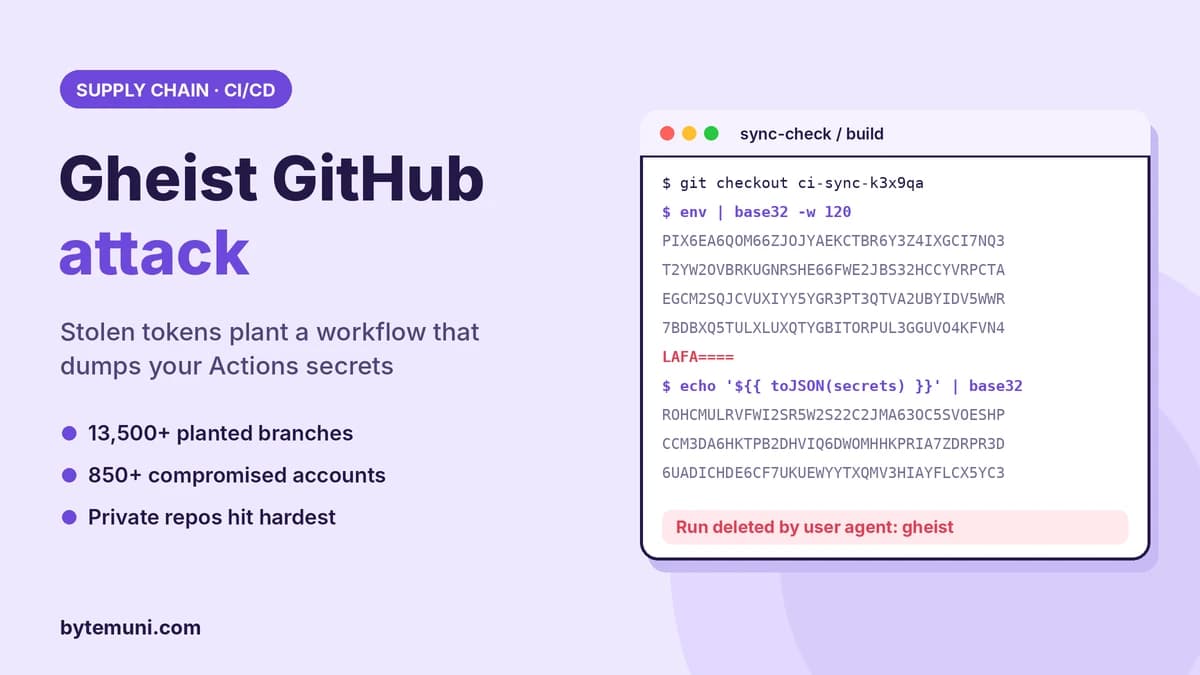
Gheist GitHub Attack: How Stolen Tokens Dump Your Actions Secrets (and How to Check in 5 Minutes)
A campaign called Gheist has planted 13,500+ secret-dumping workflows using stolen GitHub tokens. Base32 gets past log masking, permissions: {} doesn’t block access to secrets, and data leaves through GitHub’s own API. Here’s how to check your repos and lock things down.
11 min read